Tech & Reviews
Microsoft Takes Down EvilTokens Device-Code Phishing Service Tied to 12,000 Inbox Compromises
Microsoft on Tuesday announced the takedown of the EvilTokens device code phishing service that it said used artificial intelligence (AI) “at every step of the attack chain.” The action, carried out with authorization from the U.S. District Court for the Eastern District of Virginia, involved the efforts of Health-ISAC, alongside Cloudflare, Coinbase, OpenAI, Railway, SpyCloud, […]
Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate Credentials
Ravie LakshmananSep 22, 2026Supply Chain Attack / Malware Cybersecurity researchers have disclosed details of a malicious npm package named “tw-pkgprobe-7731” that masquerades as a security tool targeting developers integrating Twilio into their applications, while stealthily attempting to harvest sensitive data. The package, named “tw-pkgprobe-7731,” was first uploaded to the npm registry in mid-August 2026 by […]
WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers
Swati KhandelwalSep 22, 2026Vulnerability / Web Security WordPress has fixed a critical flaw in its core software that lets an attacker with no account make a site load a PHP file from outside its theme folders. On some servers, that can go further, allowing the attacker to run their own code. The fix shipped on […]
Check Point Warns of Management Server Zero-Day Exploited in Targeted Attacks
Swati KhandelwalSep 22, 2026Network Security / Vulnerability Attackers exploited a previously unknown flaw in Check Point’s Security Management Server in a handful of targeted attacks on July 23, the company said. The flaw, CVE-2026-93616, allows an attacker who can access the server’s web service to run scripts on it without logging in. Check Point released a […]
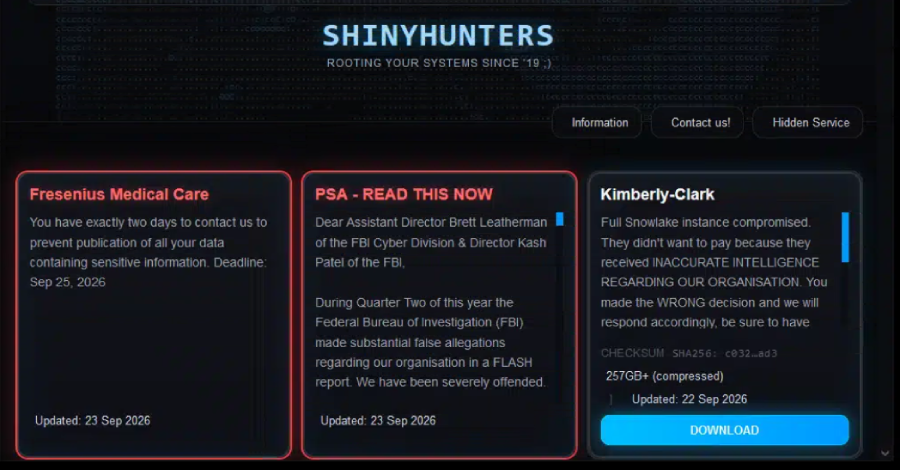
ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants
Ravie LakshmananSep 23, 2026Data Breach / Cybercrime The cyber extortion group known as ShinyHunters on Tuesday claimed it had breached the U.S. Federal Bureau of Investigation and stolen data belonging to current and former employees at the agency. “We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals […]
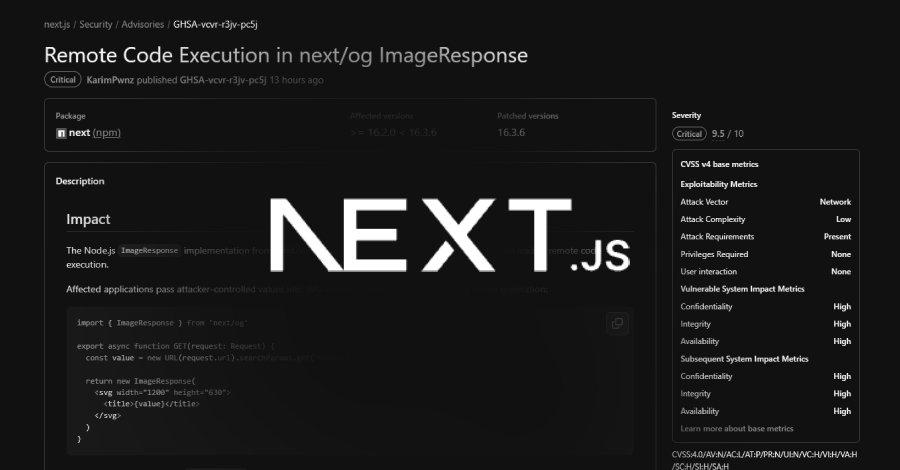
Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input
Swati KhandelwalSep 23, 2026Vulnerability / Web Security A new security vulnerability in Next.js could allow attackers to run code on a server via ImageResponse, the feature that generates Open Graph and other social preview images, Vercel said. The risk applies when an app puts values an attacker controls, such as text read from the request URL, […]
Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware
Ravie LakshmananSep 23, 2026Zero-Day / Vulnerability A Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites. The attacks, detected on September 3 and 4, 2026, involved the chaining of two vulnerabilities in Chrome (CVE-2026-85046, CVE-2026-87491) and one impacting Windows Advanced Local Procedure […]
F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth Servers
Swati KhandelwalSep 23, 2026Vulnerability / Network Security Attackers are exploiting a critical flaw in F5 BIG-IP Access Policy Manager (APM) that lets them run code on a BIG-IP system without logging in, F5 says. The flaw, CVE-2026-94127, affects only systems in which APM serves as an OAuth authorization server, issuing access tokens to applications. F5 disclosed […]
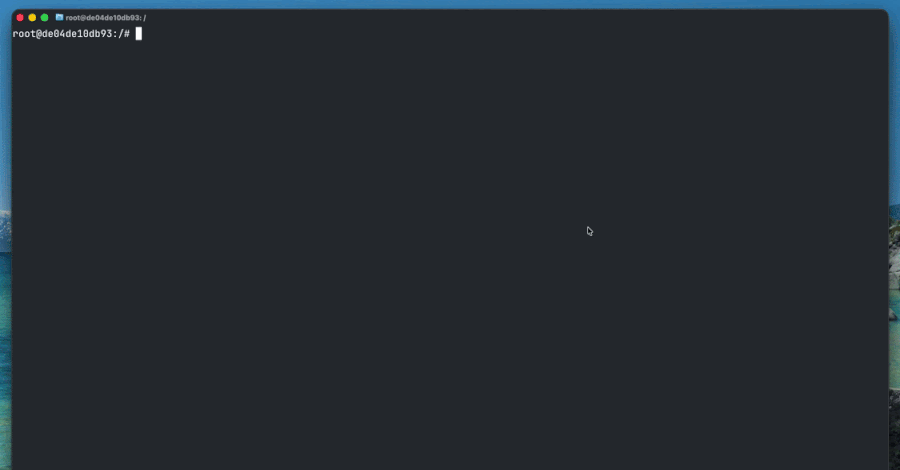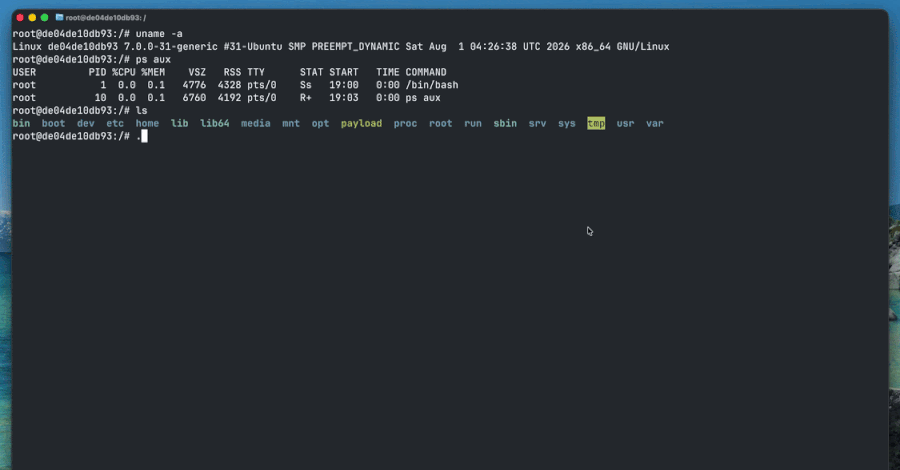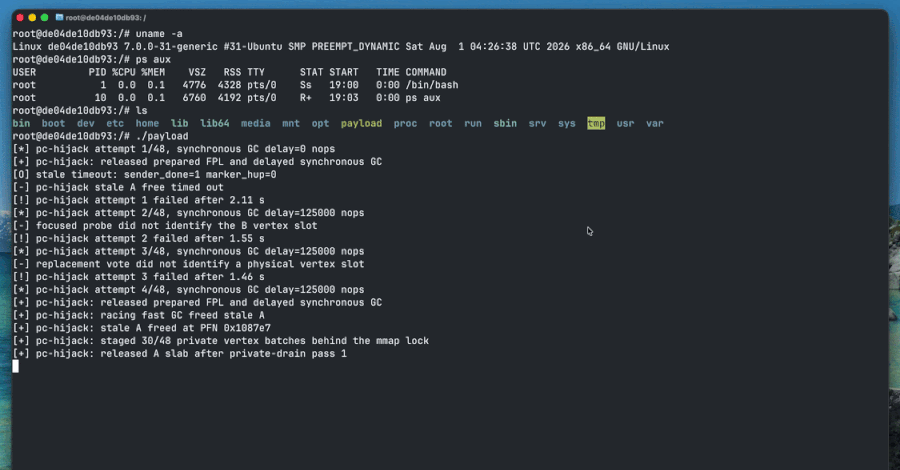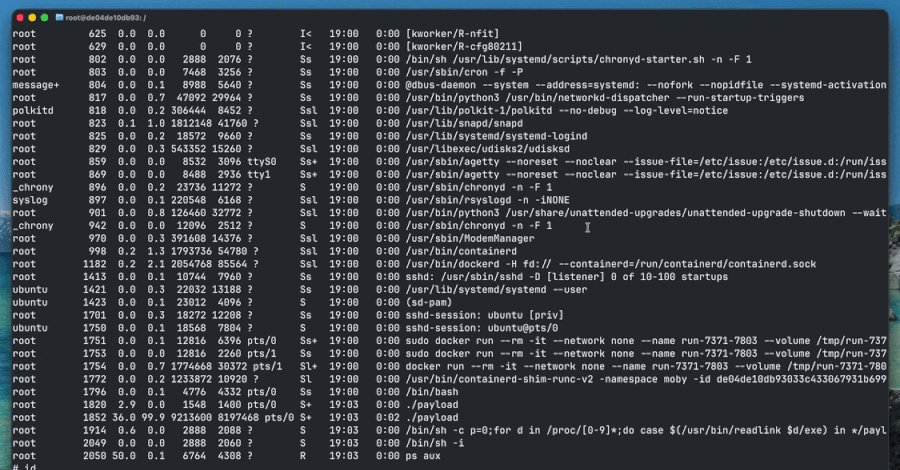
Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape
Swati KhandelwalSep 23, 2026Vulnerability / Linux A use-after-free in the Linux kernel’s AF_UNIX socket subsystem can be used to escape a container and gain root on the host, security firm DepthFirst said in research published September 22. The flaw, tracked as CVE-2026-80521 (CVSS score: 7.8), was fixed upstream on August 6, but Ubuntu has not shipped the patch […]
Anthropic and OpenAI Models Still Attempt Restricted Actions in Safety Tests
Anthropic and OpenAI on Tuesday announced new models, with both artificial intelligence (AI) companies noting that they are continuing to invest in improving alignment to combat risky behavior. Opus 5.5, per Anthropic, is a “major step up from Opus 5,” and “achieves the best scores of any model to date on our automated behavioral audit, […]